
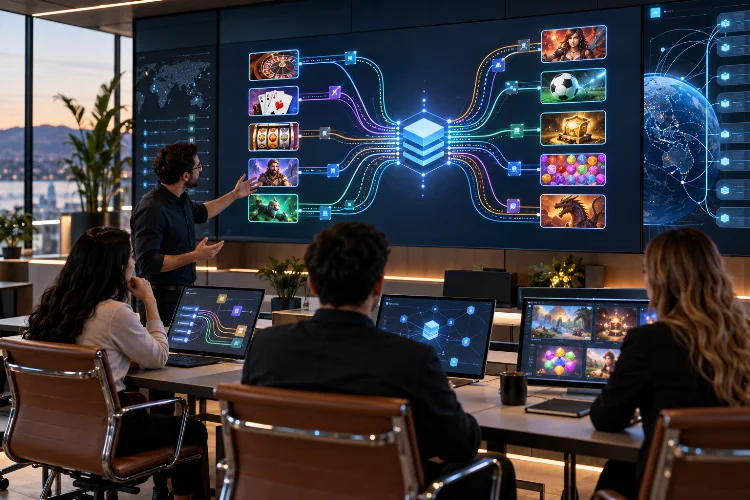
Connecting one casino game provider to an online platform is usually manageable. Connecting twenty, fifty, or even more providers is a completely different engineering problem.
Every supplier may use different endpoint structures, authentication methods, transaction identifiers, callback formats, error codes, session rules, and wallet workflows.
Without a clear integration strategy, the backend gradually becomes a collection of provider-specific exceptions that becomes harder to maintain with every new addition.
This is where advanced API design for multi-provider casino game integration becomes valuable.
Instead of allowing every supplier’s technical differences to spread across the platform, a well-designed architecture creates a stable internal contract.
Provider-specific behavior is translated at the edge, while core systems such as wallets, player accounts, reporting, and compliance work with predictable data models.
The result is not only cleaner code. Good casino API architecture can reduce integration time, prevent duplicate financial transactions, isolate provider failures, improve monitoring, and make future platform changes considerably easier.
1. Build a Normalized API Contract First
The biggest mistake in multi-provider integration is allowing external API structures to become internal platform structures.
Suppose Provider A calls a wager a bet, Provider B calls it a debit, and Provider C uses gameTransaction. Their payload structures may also represent amounts, sessions, currencies, and round identifiers differently.
The platform should not force its wallet service to understand every variation.
Instead, create a canonical internal model.
For example, the platform might standardize core operations around concepts such as StartSession, PlaceWager, CreditWin, RollbackTransaction, and GetBalance. Each external integration translates its proprietary format into that internal contract.
OpenAPI can help formalize these interfaces by describing endpoints, request structures, schemas, responses, and other API characteristics in a machine-readable specification.
A clearly documented contract also improves coordination between platform engineers and provider-integration teams.
The objective is simple: provider APIs can change, but the core casino platform should remain as stable as possible.
2. Use an Adapter Layer for Every Provider
Once the internal contract exists, each game supplier can be connected through an adapter.
Think of an adapter as a translator sitting between the provider and the platform.
A provider might send:
POST /player/debit
The adapter converts that request into the platform’s standardized wager command. The internal wallet does not need to know which supplier created the original request.
This creates strong seperation between external and internal systems.
Adapters can handle provider-specific authentication, currency formatting, game identifiers, error mapping, request signing, and unusual callback behavior without contaminating core business logic.
It also makes replacing providers easier.
If one supplier introduces a completely new API version, developers mainly update its adapter instead of rewriting wallet, player, analytics, and transaction-history services.
This pattern becomes increasingly valuable as the provider portfolio expands because complexity grows at the integration boundary instead of spreading through the entire platform.
3. Make Financial Endpoints Idempotent
Casino APIs operate over networks, and networks are not perfectly reliable.
Imagine a provider sends a wager request and the platform successfully processes it. Before the response reaches the provider, however, the connection times out.
The provider cannot know whether the wager succeeded, so it sends the request again.
Without idempotency protection, the player’s balance might be debited twice.
An idempotent operation produces the intended server-side effect only once even if an equivalent request is repeated.
HTTP defines several methods as naturally idempotent, although methods such as POST are not inherently so and often require application-level safeguards.
For financial operations, platforms can associate each wager, payout, refund, or rollback with a unique transaction or idempotency identifier.
When the same request arrives again, the server checks the identifier and returns the previously recorded result rather than repeating the transaction.
This small architectural decision can prevent some extremely expensive errors.
4. Design Retries and Failure Handling Carefully
Retries sound simple: if something fails, try again.
In distributed casino infrastructure, uncontrolled retries can actually make outages worse.
If a provider becomes unavailable and thousands of requests immediately retry several times, traffic against the failing service can multiply. That increases connection usage, CPU load, queue depth, and response latency.
Retries should therefore use limits and backoff strategies.
Persistent failures can also be isolated using a circuit breaker.
AWS describes the circuit breaker pattern as a method for preventing repeated calls to a service that is already experiencing failures or high latency. After a threshold is reached, requests can fail quickly until the dependency shows signs of recovery.
This is especially useful in multi-provider environments.
If Provider A is unavailable, its outage should not consume resources required for Providers B, C, and D.
Good API architecture expects external dependancies to fail rather than assuming every supplier will always respond normally.
5. Control Traffic With Rate Limits and Backpressure
Not every provider generates traffic at the same rate.
One supplier might send a few hundred requests per minute while another produces thousands of callbacks during peak activity. Promotional events can make those differences even larger.
API gateways can provide a protective layer between providers and internal infrastructure.
Rate limits prevent one integration from overwhelming shared backend services. AWS API Gateway, for example, supports throttling based on request rates and burst capacity, returning 429 Too Many Requests when configured thresholds are exceeded.
However, simply rejecting requests is not enough.
Financial endpoints need carefully designed retry instructions, while non-critical workloads may be routed into queues for asynchronous processing.
This is where backpressure becomes important.
When downstream services cannot process requests quickly enough, the architecture needs a controlled way to slow incoming work rather than allowing queues, databases, or connection pools to collapse.
Provider-level limits also prevent one unusually busy integration from damaging overall platform performance.
6. Use Events for Non-Critical Downstream Processing
Not every operation needs to finish before the API sends a response.
Suppose a wager completes successfully. The essential synchronous path may involve validating the session, checking the transaction, updating the wallet, and returning the result.
Afterward, several additional systems may want that information.
Analytics could record the wager. A loyalty engine might update player progress. Fraud detection may inspect the event, while reporting systems store additional operational data.
Performing all of these actions synchronously adds unnecessary latency.
Event streaming creates a better option.
Apache Kafka describes event streaming as capturing events from different sources, storing them durably, processing them, and routing them to downstream systems in real time.
The API can therefore complete the critical transaction and publish something like WagerCompleted.
Other systems consume that event independently.
This approach reduces coupling and means an analytics outage does not automatically prevent players from completing valid game transactions.
7. Plan API Versioning Before Providers Force the Issue
APIs evolve.
A provider may change authentication, add fields, replace an endpoint, modify callback behavior, or introduce a completely new protocol.
The platform also evolves internally.
Versioning prevents those changes from turning every deployment into an emergency migration.
An adapter might support Provider A’s v2 and v3 interfaces simultaneously while traffic is gradually moved to the newer implementation. Internal contracts can follow a similar strategy when breaking changes are genuinely necessary.
Backward compatibility should be preferred whenever practical.
Adding an optional response field is usually easier for consumers than renaming or removing an existing one.
Contract testing is particularly useful here. Automated tests can verify that a new adapter version still produces the canonical request and response structures expected by internal services.
This reduces the chance that a seemingly small provider change breaks games already running in production.
8. Treat API Security as a Shared Integration Requirement
Game-provider APIs frequently interact with sensitive systems.
Requests may contain player identifiers, session tokens, financial values, wager information, or other operational data.
Authentication alone is not enough.
OWASP’s API Security Top 10 highlights risks including broken object-level authorization, broken authentication, unrestricted resource consumption, security misconfiguration, and unsafe consumption of third-party APIs.
Casino platforms should therefore combine secure transport, strong service authentication, authorization checks, secret rotation, input validation, replay protection, request signing where appropriate, and detailed audit logging.
External data should also be treated as untrusted.
A request coming from an approved provider can still be malformed, duplicated, compromised, or simply incorrect.
Gaming-specific control requirements add another layer.
GLI-19 provides technical standards for interactive gaming systems and notes that such systems may consist of modular components designed to work together while maintaining appropriate controls and production configuration.
Security and compliance are easier when integration boundaries are explicit.
9. Make Every Provider Observable Independently
A platform connected to forty suppliers needs to know exactly which one is causing trouble.
Global statistics are not enough.
Imagine the overall API success rate is 98%. That number appears reasonable, but perhaps thirty-nine providers are operating at 99.9% while one major provider has fallen to 65%.
Provider-level observability reveals the real problem.
Useful metrics include request volume, latency percentiles, timeout rates, authentication failures, transaction reversals, duplicate requests, webhook delays, error-code frequency, and successful wager or payout rates.
Correlation IDs should follow requests through adapters, wallet services, databases, and downstream events.
That allows engineers to trace a failed transaction across the complete integration path instead of searching several unrelated logs.
Observability also improves commercial decisions. Persistent latency or callback problems from one supplier become measurable instead of anecdotal.
Multi-provider casino integration becomes difficult not because APIs are unusual, but because every provider is unusual in a slightly different way.
A strong architecture contains those differences behind normalized contracts and provider adapters.
Idempotency protects financial transactions, controlled retries and circuit breakers limit cascading failures, while rate limiting prevents one integration from overwhelming shared infrastructure.
Event-driven processing, thoughtful versioning, API security, and provider-level monitoring make the platform easier to scale as more suppliers are added.
Before connecting the next provider, review whether your platform has a clear canonical API model, transaction identifiers, error strategy, and observability standards.
Investing in those foundations now can turn future integrations from bespoke engineering projects into predictable, repeatable work.
