
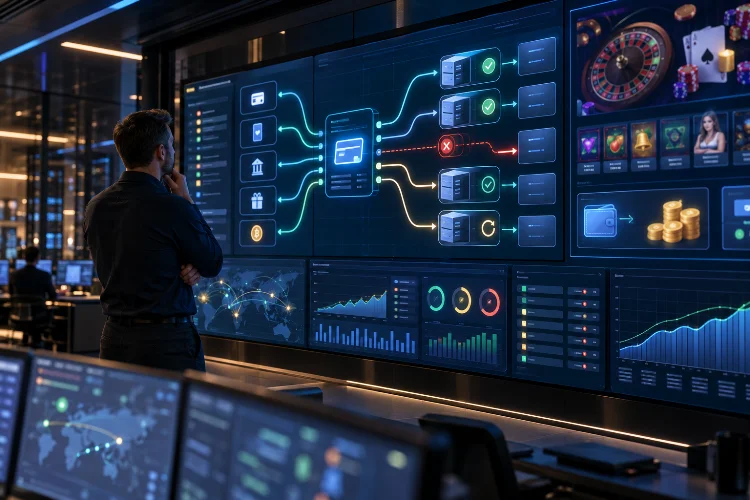
A casino deposit may look like one simple transaction, but behind the scenes it can travel through payment gateways, processors, acquiring banks, fraud systems, authentication services, internal wallets, and accounting infrastructure.
Every additional dependency creates another potential failure point.
A processor may become unavailable. A bank may decline a payment unexpectedly. A network timeout can leave the platform unsure whether a transaction completed, while a retry can accidentally create a duplicate if the architecture is poorly designed.
Understanding how payment orchestration improves casino transaction reliability means looking at the control layer sitting between the gaming platform and this complicated payment ecosystem.
Rather than integrating each payment provider independently into the cashier, orchestration centralizes routing, retries, transaction states, provider switching, monitoring, and reconciliation.
Modern routing technology can even choose between payment paths according to factors such as expected conversion or transaction cost.
The result is not simply more payment options. It is a payment infrastructure designed to continue operating when individual components do not behave perfectly.
1. Payment Orchestration Creates a Control Layer
Without orchestration, payment architecture can quickly become fragmented.
One development team integrates cards with Provider A, another connects digital wallets through Provider B, and a third builds bank payments through Provider C. Soon, every integration has different error codes, status definitions, APIs, and monitoring.
An orchestration layer provides a common interface above those providers.
The casino cashier can send a normalized payment request containing information such as amount, currency, method, customer reference, and transaction ID. The orchestration system then translates that command into the format required by the selected processor.
This separation reduces technical coupling.
Changing one processor should not require rebuilding the player’s wallet or cashier interface. Adding a new payment method can also become an integration-layer task rather than a platform-wide engineering project.
Most importantly, orchestration creates one place where routing and recovery rules can be consistently applied.
2. Smart Routing Reduces Dependency on One Processor
A payment processor can fail even when the rest of the casino platform is healthy.
Traditional architectures may simply return an error to the player. More advanced systems can evaluate whether another valid processing route exists.
This is where intelligent routing becomes valuable.
Routing engines can consider payment method, country, currency, processor availability, cost, previous performance, or historical authorization results when choosing a path.
Adyen, for example, documents intelligent payment routing that can select routes according to objectives such as conversion or cost optimisation.
Casino platforms can apply similar principles across multiple providers.
Imagine Processor A normally handles EUR card deposits. If its latency suddenly rises or availability falls, eligible transactions might temporarily move to Processor B.
This does not guarantee every payment succeeds. Banks can still decline transactions for legitimate reasons.
What routing does provide is reduced dependency on a single technical path. A provider outage becomes a localized problem rather than automatically becoming a cashier-wide outage.
3. Idempotency Makes Retries Safe
One of the most dangerous payment failures is uncertainty.
Imagine the casino sends a €50 deposit request. The processor completes it, but the network connection drops before confirmation returns.
Should the casino retry?
If it does nothing, the player’s balance may not reflect a successful deposit. If it blindly resends the transaction, the customer could potentially be charged twice.
Idempotency solves this problem.
A unique idempotency key identifies one intended financial operation. When a repeated request arrives with the same identifier, the receiving service can recognize that the operation has already been processed instead of creating another payment.
Stripe’s API, for example, supports idempotency keys specifically so requests can be retried after connection failures without accidentally performing the same operation twice.
AWS also recommends idempotency tokens for mutating operations in distributed systems so repeated requests can return the stored result rather than repeat the underlying action.
For casino payments, this protection should extend beyond deposits to withdrawals, refunds, reversals, and wallet credits.
Retries improve reliabilty only when duplication is controlled.
4. Retry Logic Should Understand Why Payments Fail
Retrying every failed transaction is not a good strategy.
Some failures are temporary. Others are final.
A timeout, unavailable processor, or temporary network failure may justify another attempt. An invalid account number or explicitly rejected transaction generally should not.
Good orchestration classifies errors before deciding what happens next.
Temporary failures might use exponential backoff, meaning the system waits progressively longer between attempts instead of repeatedly hammering a struggling service.
Stripe’s API documentation, for example, recommends exponential backoff when clients encounter request-rate limits.
More sophisticated routing can attempt another appropriate processor after certain technical failures, but this needs careful controls.
The system must avoid turning payment recovery into an uncontrolled cascade of requests across several providers.
Retry limits, provider health monitoring, circuit breakers, and idempotency should therefore work together.
Reliable payment infrastructure is not the system that retries most aggressively. It is the system that knows when retrying is appropriate.
5. Transaction States Prevent Financial Ambiguity
Payments do not always move instantly from “created” to “successful.”
Real systems contain intermediate states.
A deposit may be initiated, require authentication, remain pending, receive authorization, complete, fail, or later be reversed. Withdrawals may require even more stages before settlement.
The orchestration layer should normalize these statuses.
Otherwise, Provider A might call a transaction Authorised, Provider B uses Approved, and Provider C reports Completed, even though the underlying meanings differ slightly.
A canonical payment state model allows the wallet and front end to work with consistent concepts.
This also improves user experience.
Instead of displaying a vague error because a payment has not finished immediately, the cashier can show that processing is still underway.
Internally, state transitions should also be stored durably.
AWS guidance for payment systems emphasizes persistently storing and idempotently processing customer transactions to maintain data integrity.
Its event-driven reference architecture uses loosely coupled services and failure isolation so payment-related processing can continue reliably.
Clear states reduce uncertainty for both players and operations teams.
6. Event-Driven Processing Improves Resilience
Not every task needs to happen during the initial deposit request.
Suppose a payment completes successfully. The platform may then need to update analytics, generate accounting records, notify fraud systems, send confirmation messages, and initiate reconciliation workflows.
Waiting for every downstream service would make the player’s payment slower and more fragile.
Event-driven architecture separates these concerns.
The essential payment transaction can complete first, after which events such as DepositCompleted are delivered to downstream systems.
AWS’s payment architecture guidance uses event-driven components to create loosely coupled, independently scalable, fault-tolerant payment workflows.
However, event systems commonly operate with at-least-once delivery, meaning the same event may occasionally arrive more than once.
AWS’s transactional outbox guidance explicitly notes that consumers should be idempotent when duplicate message delivery is possible.
This is why orchestration, event processing, and idempotency should be designed together rather than as seperate technical concerns.
7. Reconciliation Detects What Automation Misses
Even excellent real-time systems can develop discrepancies.
The casino might record a payment as successful while a later processor report shows a reversal. A webhook may fail to arrive. Settlement records may contain adjustments that were not visible during initial authorization.
Reconciliation catches these differences.
The process compares the casino’s internal ledger with data from payment processors, banks, and settlement systems.
Suppose internal records show 25,000 completed deposits, but processor settlement data contains only 24,994. Those six exceptions require investigation.
Automated reconcilliation can identify such mismatches quickly rather than expecting finance teams to manually compare huge transaction files.
Orchestration makes this easier because transaction information from multiple providers can be normalized into a consistent internal format.
This becomes increasingly important as payment options expand.
The UK Open Banking Standard, for instance, currently defines APIs for secure payment initiation and other financial interactions between authorized participants; version 4.0.1 was published on March 18, 2026.
Every new payment rail increases choice, but it also increases the need for reliable financial matching.
8. Security Has to Follow Every Payment Route
Multi-provider routing should never weaken payment security.
More integrations mean more credentials, endpoints, webhooks, tokens, and systems capable of interacting with financial information.
PCI DSS remains a major security framework for environments that store, process, or transmit payment card account data. PCI SSC published PCI DSS v4.0.1 as a limited revision of v4.0, clarifying existing requirements without adding or removing requirements.
A good orchestration design can help reduce exposure.
Sensitive payment details can remain within specialized payment environments while internal casino systems work with tokens or provider references instead of raw card information whenever appropriate.
Access should also follow least-privilege principles.
One service responsible for routing transactions should not automatically receive unnecessary access to every wallet function or financial database.
Security architecture must follow the transaction regardless of which processor handles it.
Reliability without security is not meaningful payment reliability.
9. Provider-Level Observability Finds Failures Faster
A payment platform needs to know more than its overall approval rate.
Imagine Provider A is processing successfully at 98%, Provider B at 97%, and Provider C has suddenly fallen to 52%.
A platform-wide average may hide the problem for too long.
Provider-level monitoring should track latency, technical failure rates, bank declines, authentication outcomes, timeout frequency, retry volume, webhook delays, and routing changes.
This information can feed routing decisions.
If one provider’s latency rises dramatically, the orchestration engine can flag or potentially reduce traffic to that route according to established rules.
Good observabilty also makes incident investigation much faster.
Every transaction should have identifiers that allow support and engineering teams to trace its journey from cashier request to orchestrator, processor, wallet, and settlement records.
That creates something payment systems badly need: explainability.
When money appears to be missing, “something probably timed out” is not an acceptable diagnosis.
10. Reliability Also Includes Customer-Fund Controls
Transaction reliability is not limited to whether APIs remain online.
Operators also need confidence that financial records correspond to properly controlled customer funds.
In Great Britain, Gambling Commission guidance requires operators subject to customer-fund rules to keep relevant customer funds in accounts separate from business accounts. Operators must also disclose information about the level of customer-fund protection.
This highlights an important architectural distinction.
The orchestration platform moves payment instructions, but it must remain aligned with the wallet ledger, treasury records, settlement systems, and regulatory accounting.
A successful API response is not the end of the transaction lifecycle.
Funds may still require settlement, reconciliation, withdrawal processing, or accounting classification.
Strong orchestration connects operational reliability with financial traceability.
Payment orchestration improves casino transaction reliability by turning a collection of external payment providers into a controlled financial ecosystem.
Smart routing reduces dependence on individual processors, while failover strategies help contain outages.
Idempotency makes retries safer, normalized transaction states eliminate ambiguity, and event-driven processing keeps secondary workloads away from critical payment paths.
Reconciliation, security controls, and provider-level monitoring then ensure that transactions remain traceable long after the initial API response.
The goal is not simply to maximize successful deposits. Reliable payment infrastructure must produce predictable, secure, and auditable outcomes across deposits, withdrawals, refunds, and reversals.
For iGaming teams evaluating their payment stack, start by tracing what happens when the primary processor fails mid-transaction. If the answer is uncertain, payment orchestration is likely an area worth strengthening.
